DPDP StarDPDP Star

DPDP Act, 2023. Main duties from 13 May 2027.

Four parts of trust. One star. — DPDP Act 2023 Consent Management System

DPDP Star is a Consent Management System. It records each visitor’s choice, and keeps withdrawals, requests and team actions in a tamper-evident chain on a server in India.

Request early access 14-Point CMS Guide See how it is built

  • Confidentiality
  • Integrity
  • Availability
  • Safety

Anatomy

How it looks, and how it is done.

Four goals, Confidentiality, Integrity, Availability and Safety, for consent that is easy to give, easy to withdraw and on record. Hosted in India, with tamper-evident, blockchain-anchored records. Why DPDP Star

Confidentiality

Easy to give. Easy to take back.

Accept, reject or choose in one step.

Withdraw from the privacy page, as easily as you gave.

Only your team, by role, sees the record.

Email addresses and phone numbers kept for your team and your organisation are stored encrypted.
Integrity

A trail built to show a change.

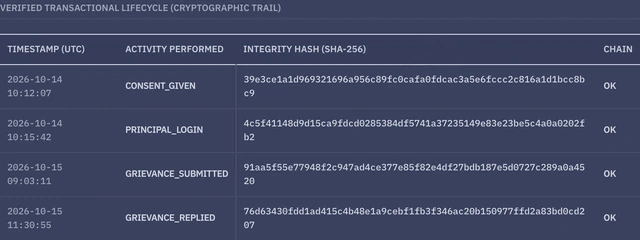
A tamper-evident chain: each withdrawal, request and team action is cryptographically chained to the one before.

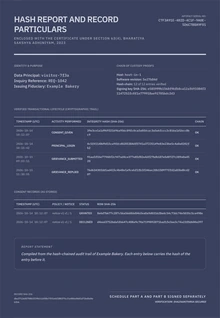
The DPO hash report checks every entry.

Banner choices are listed in it with their own fingerprint.

Daily blockchain anchoring and independent trusted time-stamps. Live

Availability

Rooted in India.

Runs on a server in India, from CynorSense, Hyderabad.

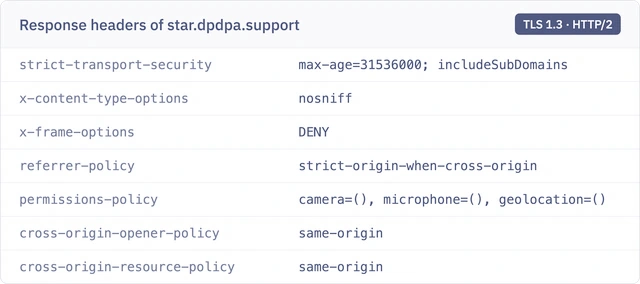
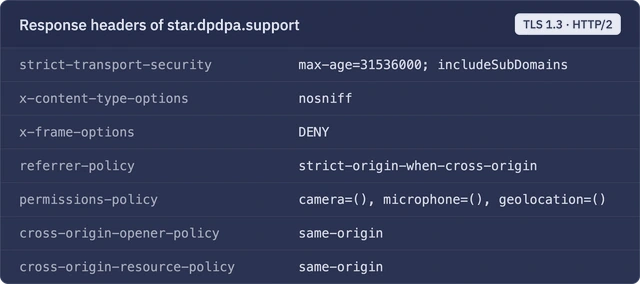
HTTPS only, with strict transport security.

Where it runs, in plain view.

Safety

Built for your duties. Drafted for you to review.

A privacy policy draft, read from your own site, for you to review.

Your purposes, your notice.

The decisions stay yours.

Breach alerts are built for CERT-In’s 6-hour incident reporting window.

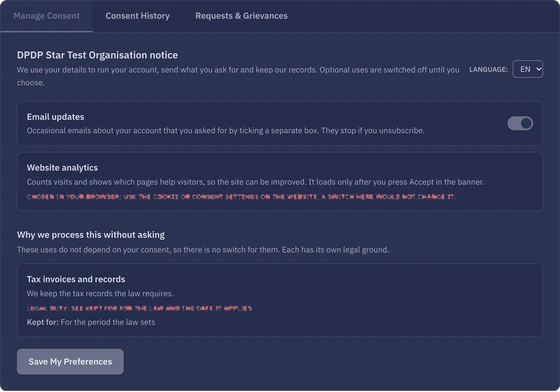
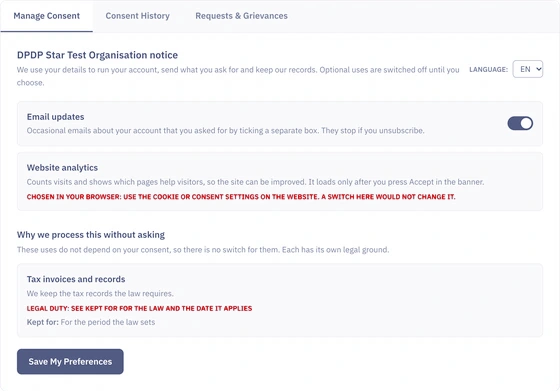
My Privacy Dashboard with the consent choices of a test visitor.My Privacy Dashboard with the consent choices of a test visitor.
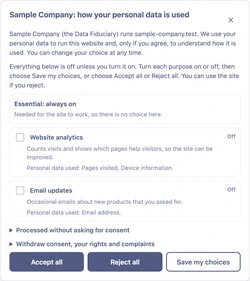
The consent banner on a test site, with Accept all, Reject all and Save my choices.The consent banner on a test site, with Accept all, Reject all and Save my choices.
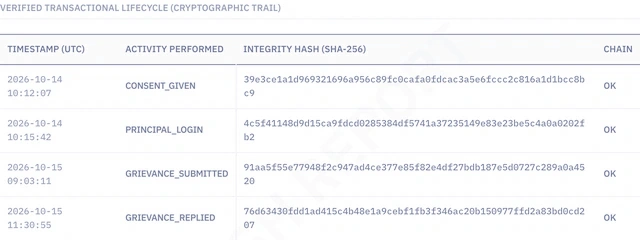
The verified lifecycle of a test visitor: each entry with its cryptographic fingerprint and a chain check.The verified lifecycle of a test visitor: each entry with its cryptographic fingerprint and a chain check.
The hash report for a test visitor, listing the chain and the stored consent records.The hash report for a test visitor, listing the chain and the stored consent records.
The response headers of star.dpdpa.support: TLS 1.3, strict transport security, no sniffing, no framing.The response headers of star.dpdpa.support: TLS 1.3, strict transport security, no sniffing, no framing.
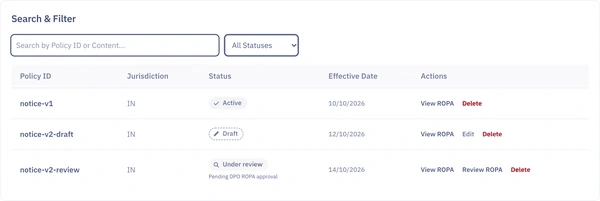
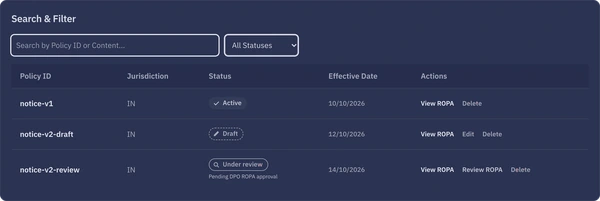
The policy list of the console showing a draft, a policy under review and an active policy.The policy list of the console showing a draft, a policy under review and an active policy.
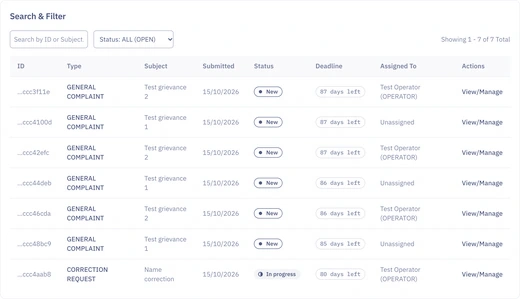
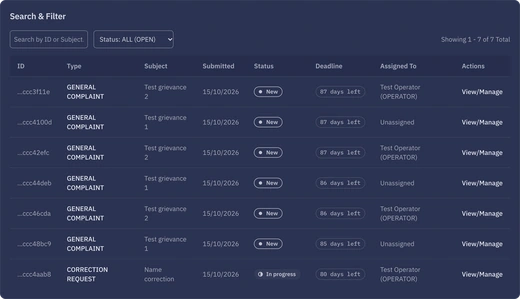
The grievance list of the console with test grievances, statuses and deadlines.The grievance list of the console with test grievances, statuses and deadlines.

Real screens, with test data: a fictional Example Bakery and its visitors.

Every choice, kept. Every request, answered. Every record, checkable.

Covered

The main duties of the Act, and the trust infrastructure around it.

The duties

  • s.5 Notice
  • s.6 Consent
  • Withdrawal
  • s.8 Safeguards and records
  • ss.11 to 13 Rights of the Data Principal
  • Grievance redressal
  • Breach register

The ways in

  • Consent banner Live
  • Privacy page Live
  • Wix app Coming to the Wix App Market
  • SMS consent Coming soon
  • WhatsApp consent Coming soon
  • QR consent Built, being tested
  • Mobile apps, iOS and Android Coming soon
  • ROPA tools and data-flow map Coming soon

Trust & evidence infrastructure

  • Hosted in India Live
  • Blockchain-anchored evidence Live
  • Digital signatures Live
  • Independent trusted time-stamps Live
  • CERT-In 6-hour incident reporting Live
  • Automatic multilingual notices in Indian languages Planned

Source: DPDP Act, 2023, sections 5, 6, 8, 11 to 13

Why now

Be ready.

13 May 2027

Source: G.S.R. 843(E), 13 November 2025

What ready means

  • s.6Consent and withdrawalBanner and privacy page
  • s.8Safeguards and recordsThe tamper-evident chain and the audit log
  • ss.11 to 13Rights and grievancesOne list for your team
  • Your callWhat to do about a requestThe decision stays with you

Request early access now, then add your site and answer requests as each step opens.

Where consent is the basis, withdrawing must be comparable in ease to giving it. If it is questioned in a proceeding, you must prove you gave notice and got consent.

Where people gave consent, or data for a stated use, they can ask for a summary of it. They can ask to correct, update or erase it.

You must give people a way to raise a grievance and publish your answer time. From 13 May 2027 it can be at most 90 days.

Source: DPDP Act, 2023, sections 6(4), 6(10), 7(a), 8(10), 11 to 13; DPDP Rules, 2025 (G.S.R. 846(E)), rules 1(4) and 14(3); G.S.R. 843(E)

How it works

Three steps to answering requests.

  1. 01

    Register your organisation

    Submit your business name, work email, sector and size on the self-service Early Access page, confirm the 6-digit verification code sent to your email, and set up your password and authenticator app.

  2. 02

    Add your site. Prove it is yours.

    Add your website domain in the console and verify ownership via a DNS TXT record or HTML meta tag. Once ownership is verified, install the embed script or platform plugin on your site.

  3. 03

    Answer requests

    Requests and grievances from your visitors reach your team. You reply, and the decisions stay yours.

    The grievance list of the console with test grievances, statuses and deadlines.The grievance list of the console with test grievances, statuses and deadlines.

Every site requires domain ownership verification before the consent banner and privacy page activate for your domain.

Request early access Get the 14-Point Guide by Email

India, giving consent

The moments where consent is asked.

A checkout, a front desk, a check-in, an admission form. Each is a notice, a choice, and a way back, and the record is kept.

01

D2C and online shops

A shopper at checkout

Checkout page

Example Store uses your email and address to deliver your order. Offers by email stay off unless you turn them on.

Save my choices

Recorded. You can change this on My Privacy Dashboard.

02

Hospitals and clinics

A patient at the front desk

Scan the code at the desk to read the notice and choose. Built, being tested

SMS Coming soon

Example Clinic: how we use your number for appointment reminders. Read and choose.

Reminders on

Recorded.

03

Hotels and wellness centres

A guest at check-in

Scan the code at the desk to read the notice and choose. Built, being tested

WhatsApp Coming soon

Example Hotel: how we use your details for your stay. Read and choose.

Stay updates on, offers off

Recorded.

04

Hostels

A student at admission

My Privacy Dashboard

Your choices at Example Hostel: warden messages on, offers off.

Erase my data

Request GRV-1042 sent. In progress. Your team replies from the console.

05

Schools

A parent on the admission form

Parent check decided by your DPO from your own records Live

Parent check through a government-issued digital ID Planned

Admission form

Example School uses your child’s details to manage admission and fees. Read the notice.

Parent’s choices saved

Recorded. You can withdraw on My Privacy Dashboard.

06

Marketing and advertising

A person signing up to a campaign

Withdrawn: offers by email. Recorded on My Privacy Dashboard.

In-app consent sheet Coming soon

Example Campaign: may we send you offers? You can say no.

Not now

Illustrative scenes with fictional businesses. They are not customers. Where a scene shows a channel that is not built yet, it carries a Coming soon tag.

01 · Rights and grievances

People ask; your team answers on time.

A rights portal is live at dpdpa.support/rights. Reminders go out before the 90-day limit (Rule 14(3)).

Live rights portal and grievances

  1. 1Withdraw from the privacy page as easily as you gave consent.
  2. 2Every grievance shows its deadline.
My Privacy Dashboard with the consent choices of a test visitor.My Privacy Dashboard with the consent choices of a test visitor.
The grievance list of the console with test grievances, statuses and deadlines.The grievance list of the console with test grievances, statuses and deadlines.

02 · Notices and your record of processing

Your notice and your ROPA, kept together.

Each consent stores the notice version and its hash. The ROPA has a completeness check.

Live notices and ROPA

  1. 1The active notice version, stored with each consent.
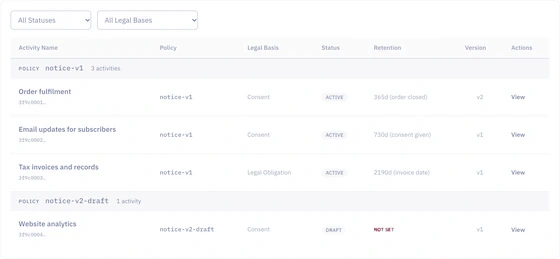
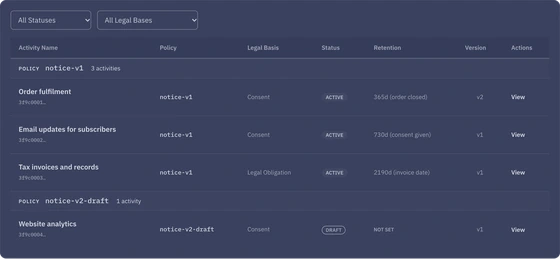
  2. 2The ROPA check flags what is missing, such as a retention period.
The policy list of the console showing a draft, a policy under review and an active policy.The policy list of the console showing a draft, a policy under review and an active policy.
The register of processing activities with test entries, grouped by notice.The register of processing activities with test entries, grouped by notice.

03 · Breach and evidence

When something goes wrong, a record you can stand behind.

48 h and 72 h reminders, a PDF record and a CSV to notify. A signed evidence report to support your Section 63(4) Bharatiya Sakshya Adhiniyam certificate. It is not the certificate.

Live breach register Live signed hash report

  1. 1Download the record as a PDF.
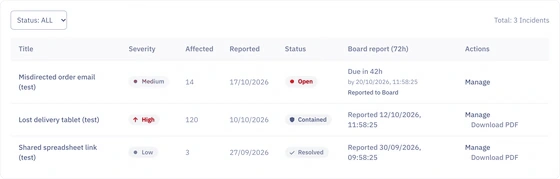
  2. 2The 72 hour countdown to the Board report sits on the row.
  3. 3Each link of the chain is checked in the hash report.
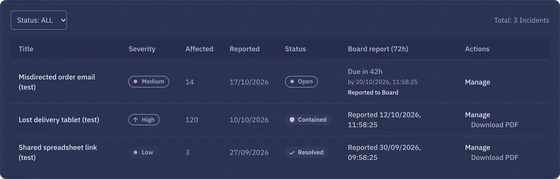
The breach register with three test incidents and the 72 hour Board report countdown.The breach register with three test incidents and the 72 hour Board report countdown.
The hash report for a test visitor, listing the chain and the stored consent records.The hash report for a test visitor, listing the chain and the stored consent records.

04 · Erasure and the audit trail

Erase on request; show every change.

Erasure completes only with your DPO’s approval. Each organisation has its own tamper-evident chain.

Live erasure with approval Live tamper-evident chain

  1. 1An erasure request waits for your DPO’s approval.
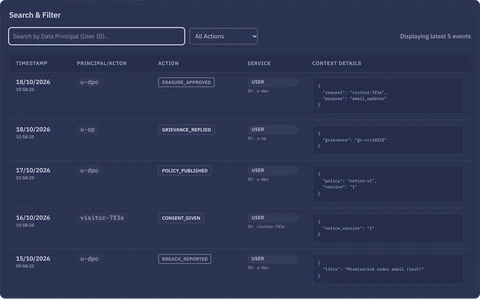
  2. 2Each action is written to the audit trail.
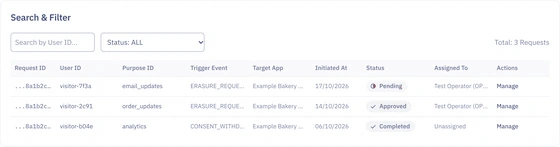
The erasure request list with test requests and their statuses.The erasure request list with test requests and their statuses.
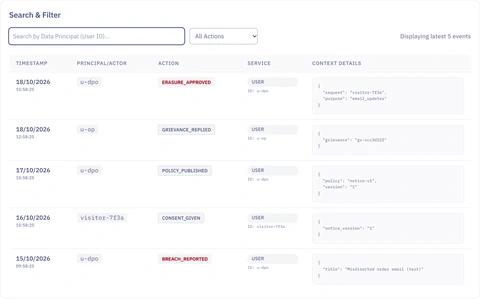
The audit trail with test events and their context.The audit trail with test events and their context.

05 · Children (section 9)

A parent decides for a child.

Your DPO approves each parent check from your own records. A check through a government-issued digital ID is planned.

Live parent check decided by your DPO Planned government-issued digital ID check

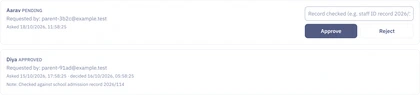
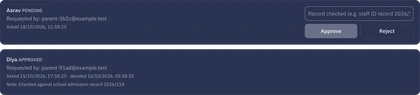
  1. 1Your DPO approves or rejects the parent check.
  2. 2The record checked is written down with the decision.
The parent verification queue with a pending and an approved test request.The parent verification queue with a pending and an approved test request.

06 · The console for your team

One console, three roles.

DPO, Operator and Admin roles. An Operator sees only the work assigned to them. Reports export.

Live DPO, Operator and Admin

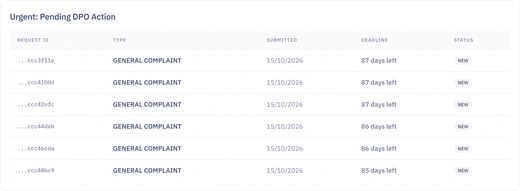
  1. 1Pending actions and their deadlines, on one screen.
  2. 2Reports export as files.

Live Sign-in recovery works with MFA recovery codes.

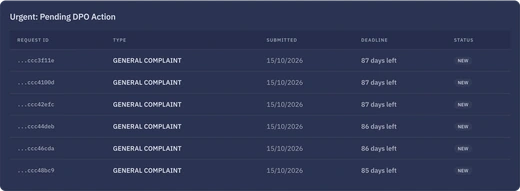
The DPO dashboard with the pending actions of a test organisation.The DPO dashboard with the pending actions of a test organisation.
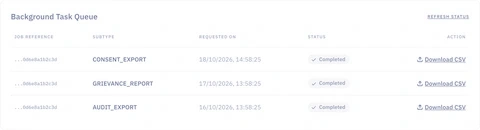
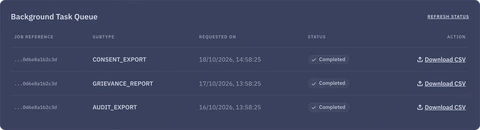
The background task queue with test exports.The background task queue with test exports.

Integrations

Works where your data already lives.

Register your organisation first, then connect in one click from your platform marketplace or console.

Names and logos are trademarks of their owners; no partnership or endorsement implied.

What you will get

What is live, and what is next.

Built and running today

  • Live A consent banner and universal embed script that record every choice
  • Live A privacy page for requests and grievances
  • Live One list for your team, with a breach register
  • Live A per-organisation tamper-evident chain and the DPO hash report
  • Live A server in India

Open now: self-service early access registration, domain ownership verification, universal embed script for any website, and CMS plugins for WordPress, WooCommerce, Shopify, Joomla and Drupal.

Coming next

  • SMS and WhatsApp consent messages Coming soon
  • QR consent at the desk Built, being tested
  • Consent from mobile apps, iOS and Android Coming soon
  • Plug into the ROPA tool you already use, and see how personal data flows through your app. Coming soon

Sources

Banner

Privacy page

Your site’s apps

Purposes

Order updates

Analytics

Offers by email

ROPA record

Record of processing activities

14 Essential Points · Architecture & Evidence Guide

What every Consent Management System must always have.

Before selecting a consent tool, verify that it delivers cryptographic proof, legal verification signature certificates, DPO-gated erasure with legal caution, and trust & evidence infrastructure.

Email me the 14-Point Guide Sent automatically as a private 72-hour link
  • PCA (Personal Consent Artifact)Downloadable, cryptographically verifiable receipt for every Data Principal choice.
  • Legal Verification Signature CertificateDigitally signed evidence report to support your Section 63(4) Bharatiya Sakshya Adhiniyam certificate.
  • Compliance & ROPA CheckerAutomated Record of Processing completeness checks with missing-retention flags.
  • Erasure with Caution to LegalDPO approval gate with statutory retention & legal-hold cautions (Rule 8(3)).
  • Tamper-Evident SystemTamper-evident, cryptographically chained records for each organisation, with daily blockchain anchoring.
  • Trust & Evidence InfrastructureBlockchain-anchored records, digital signatures, independent time-stamps & CERT-In 6-hour incident reporting.

DPDP StarDPDP Star

Put your consent and rights handling in one place.

Register for early access, verify your domain, and deploy the consent banner on any website or CMS platform.

Request early access Get the 14-Point Guide by Email

Already registered? Sign in. Works with any website via our embed script and with WordPress, WooCommerce, Shopify, Joomla, Drupal and Wix. From CynorSense Solutions Private Limited, Hyderabad, India.

DPDP Star is a Consent Management System for the Digital Personal Data Protection Act, 2023, made by CynorSense Solutions Private Limited, Hyderabad. It records each visitor’s consent choices and keeps withdrawals, rights requests, grievances and team actions in a tamper-evident chain, for your team to answer from one console. It runs on a server in India. It helps with your duties under the Act; it does not, by itself, make an organisation compliant.

Questions and answers
Does DPDP Star make my organisation compliant?

No. DPDP Star helps you carry out duties under the Digital Personal Data Protection Act, 2023. It does not, by itself, make a site or an organisation compliant. The notices you publish and the decisions you take on requests remain yours.

Is DPDP Star a Consent Manager?

No. DPDP Star is not a Consent Manager under the Act. Your organisation stays the Data Fiduciary, the one that decides why and how personal data is used. DPDP Star is software, not legal advice.

Who answers a visitor's request?

You do. The privacy page takes the request and the console shows it to your team. Your team replies from there and decides what to do. DPDP Star does not decide for you.

Do I need a Data Protection Officer to use it?

No. The console has a Data Protection Officer role, an Administrator role and an Operator role, and one person can hold both the Data Protection Officer and Administrator roles in a small organisation. Section 10 of the Act requires a Data Protection Officer only of a Significant Data Fiduciary, a class the Central Government names. From 13 May 2027, every Data Fiduciary must still publish the contact of a Data Protection Officer, if it has one, or of a person who can answer questions about its processing (section 8(9)).

What does a plan change?

No plan switches off consent, notice, privacy policy, rights request or grievance features: today every plan, including Free, has them. Plans differ in team logins: the Free plan has none, so you answer requests and grievances from your Wix dashboard or self-service console; Starter has 1, Standard 3 and Growth 10. The people and ways-of-use sizes are a guide, not a cap. Features we add later may need a paid plan; we will show this on the pricing page first.

What do I need to request early access?

Your business name, work email, sector and the size of your organisation. Submit the self-service registration form on the Early Access page with proof-of-work verification, confirm your work email with the 6-digit code, and set up your password and authenticator app.

Which websites does it work with?

DPDP Star works with any website through our universal embed script (WordPress, WooCommerce, Shopify, Joomla, Drupal and custom web apps) after DNS TXT or HTML meta-tag domain ownership verification, as well as Wix sites via DPDP Star for Wix.

Where is the data kept?

On a server in India. Strict per-organisation data isolation means each organisation sees only its own data; the checks that enforce this run on the server for every request.

What does tamper-evident mean?

Each withdrawal, request, grievance and team action is cryptographically chained to the one before in a tamper-evident record kept separately for each organisation, with daily blockchain-anchored evidence and independent trusted time-stamps. If an entry is changed later, the chain no longer matches, and the DPO hash report shows it. It shows a change; it does not stop one.

What does it cost?

You can start on the Free plan at no charge via Early Access. Paid plans (Starter, Standard, Growth and Enterprise Self-Hosted) scale by team logins, annual Data Principal volume and processing purposes across Wix, Shopify, WordPress, WooCommerce and custom web stacks. Enter your work email on the Pricing & Plan Guide page to receive the full pricing schedule and 14-Point Architecture Guide.

Does it do SMS, WhatsApp, QR codes or mobile apps?

Not yet. Coming soon: SMS and WhatsApp consent messages, a mobile app SDK for iOS and Android, ROPA tool integration and a map of data flows. QR consent at the desk is built and is being tested. The web consent banner, privacy page, embed script, integration APIs and console are built and running.

What is a Personal Consent Artifact (PCA) under the DPDP Act?

A Personal Consent Artifact (PCA) is a downloadable, cryptographically verifiable receipt generated for every Data Principal choice (grant, update or withdrawal). It records the notice version, selected purposes, timestamp and a cryptographic fingerprint so both the Data Principal and the Data Fiduciary can verify the record under Section 6(10) of the DPDP Act, 2023.

How does DPDP Star handle Section 63(4) Bharatiya Sakshya Adhiniyam (BSA) electronic evidence?

DPDP Star produces a digitally signed evidence report to support your Section 63(4) Bharatiya Sakshya Adhiniyam certificate. Your Data Protection Officer or authorised officer can enclose it with the certificate they sign. DPDP Star does not issue the certificate, and admissibility is always for the court to decide.

How does DPO-gated erasure with legal caution work?

When a Data Principal requests erasure under Section 12(3), DPDP Star places the request in a DPO approval queue with automated statutory retention checks, active legal-hold warnings and minimum one-year log retention reminders under Rule 8(3) of the DPDP Rules, 2025, ensuring records required by law are not prematurely deleted.

The Ask DPDP Star helper, at the bottom right of larger screens, answers from these. For anything else, write to [email protected].

Request early access